
Thursday, May 02, 2013
Evolving Role of IT for Risk and Assurance Professionals
This is a full day conference scheduled to be held at 6th May, 2013 at Hilton Colombo Residence.


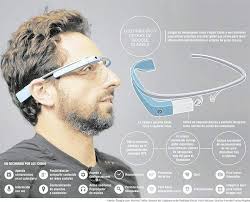
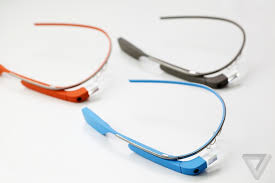
Google Glass Hacked...!
Google glass made very interesting headlines during last couple of months. There was lot of expectations and anticipation regarding this new piece of device from Google. But, disappointing to note, that this testing device been jailbroken by infamous Android and iOS hacker named Jay Freeman (aka Saurik)
http://www.kitguru.net/channel/joseph-mcdonnell/google-glass-jailbroken-hacker-says-security-is-ineffective/#.UYDeGcIoFLc.facebook

http://www.kitguru.net/channel/joseph-mcdonnell/google-glass-jailbroken-hacker-says-security-is-ineffective/#.UYDeGcIoFLc.facebook
Tuesday, March 13, 2012
Kia Picanto 2012


Kia Picanto is very stylish compact car which can easily accommodate 4 average size adults. This new design with the latest features capture the current market quickly. Very rarely we see a latest Picanto in Sri Lankan roads, but there are more than 180 car orders placed at the moment and will populate our roads with Kia Picanto 2012 model in few months time.
Kia Picanto comes in 4 speed auto and 5 speed manual. There are three engine types.
KAPPA 1.2 MPI Engine - manual
max 87 ps at 6,000 rpm
KAPPA 1.0 MPI Engine - manual
max 69 ps at 6,200 rpm
KAPPA 1.0 FFV Engine
max 80 ps at 6,200 rpm
Sunday, November 20, 2011




Tuesday, October 25, 2011
Why penetration testing information should be destroyed?
Penetration testing is a sensitive testing mechanism against organizational assets. Penetration testing focuses on the current infrastructure of an organization network and its weaknesses. This test is able of identified most sensitive information security weaknesses of organizations’ network infrastructure. This sensitive information is very critical to organizations and protecting this from unwanted hands is utmost priority. When a penetration testing assignment is underway, it is important to reveal most of the business critical operations, information, critical assets, resource persons, etc to penetration testing team. On the other hand, during their penetration testing process, penetration-testing team can learn many hidden vulnerabilities, security weaknesses, and business process weaknesses and many more. These hidden weaknesses can create catastrophe event to organization without any notification, if goes to intruders or malicious users hands. Although the criticality of this information is very high, organization cannot do penetration testing with their internal teams. This is due to lack of experience, exposure, qualifications, equipments, knowledge of internal teams or lack of personal resource availability within the organization. Hence, organizations have to go for external resources by taking a slight risk. However, many of these risks can be covered via appropriate legal bindings, and selecting reputed, qualified, and professional team of penetration testers. Organizations must draft appropriate legal terms and bindings and get third parties abide by them to protect the organization that they may face in case of breach of confidentiality. In the normal practice and depending on the sensitivity of the information client organizations and third party penetration testing team can agree to destroy the information gathered during the penetration testing process. Furthermore, it should be noted, that client organization must specifically mention the information that they wanted the service provider (penetration testing team) to destroy and the period of time that the penetration testing team can retain confidential data before destroying. On the other hand, it should be clearly define the process to destroy, and confirmation of destroy, etc.
In case, if the external penetration testing team does not destroy the information, it is an unprofessional behavior of that origination or the team, and they might face legal charges or imprisonment depending on the case. Penetration testing team can be victims of, negligence of duties, breach of confidence, reputational damages, and legal actions. Since, the criticality of the information it is advised to destroy the collected information. For instance, if an attacker infiltrate penetration testing team member’s laptop where critical data is stored, attacker can extract very valuable first hand information from without much difficulty. This information can be used against the client organization to blackmail, threaten, attack, steal more information, and selling extracted information to third parties (hackers, competitors), etc.
It is imperative to select very reputed and professional team of penetration testers for your penetration testing projects. Below given are few ways to gauge the penetration testing vendor.
· Check whether the penetration testing is their core competencies. Some organizations provide this as a value added service and not master in the area.
· Check for the real world implementation and experience, rather than paper qualifications of testing team
· Evaluate vendors trustworthiness and competence
· Consider the cost versus frequency of penetration testing needed to conduct
· Find real penetration tester who are expert in the field and have practical experience in real environment, this is difficult to find but it will be worth the test
· Ask for references from vendor and verify their status
· Perform a thorough background check to identify the real nature of the vendor
Session fixation
Web applications use a mechanism called session management to maintain user’s web experience more smooth and easy. Web servers’ use unique identifier called Session ID to identify users separately. Each user is been granted with a unique session ID upon request to open a connection with a web service. Commonly session IDs are maintain by use of session IDs in a URL, session IDs in a hidden form field or store in cookies. These IDs are given a time to expire in some cases. Many of the cookies are not only identifiers but also act as an authenticator. This enable the interest to attackers, if they can grab the cookies and establish the session, they can take act as a legitimate user. This helps them to carry out unauthorized activities. This method is called session hijacking, where attacker takeover some legal users session and act as a legitimate user. Hence, it is necessary to provide web session security. Web session security is trying to prevent mainly three types of web attacks; those are interception, prediction and brute forcing. Session fixation attack is a three-step process
1. Session setup - The attacker sets up a "trap-session" for the target web site to extract the session's ID or select an arbitrary session ID for the attack. In some cases, the established trap session value must be maintained (kept alive) with repeated web site contact.
2. Session fixation - The attacker introduces the trap session value into the user's browser and fixes the user's session ID.
3. Session entrance - The attacker waits until the user logs into the target web site to fix the session ID value and take over the session by the attacker.
Below listed few ways in which the session fixation can be mitigated.
1. User built in session frameworks - most of the application framework comes in a session management scheme. These generate session IDs and manage them pretty well. These mechanisms are well tested by security professionals and fixed most of the vulnerabilities. Hence, these are much better than the homegrown session managements, due to above reasons.
2. Store session data on severs - any program language provide a way to store session data in objects. These session objects can be stored in servers to prevent attacks.
3. Be aware of the data in the session objects. - Programmers need to be aware of where and what data they store in session objects. These can be DBs, file systems, or RAM. There can be many standards violation (for instance, PCI-DSS, ISO 27001). You can consider encrypting data that is being stored in session objects.
4. Short session timeout sessions - session timeout interval is generally configured in servers. If the time that the session be active without activities can be reduce, where it can reduce the time that left for attackers to steal, copy, of hijack the session IDs.
5. User session ID with enough entropy and length - most built-in session ID frameworks use random session IDs that are difficult to predict due to the long length.
6. Invalidate session on the server - although users and applications clear cookies at their log out from sites, it does not necessarily kill the session on the server. Malicious attackers use session ID replay to gain access to that particular session. This can be avoided with implementation of Session.Abandon() (ASP,.Net), or session.invalidate (J2EE), which kill sessions on the server when users log out.
7. Regenerate session when privileges changes - when the privileges of user changes, sessions should be change. For instance, when a user log in his privileges changes and when users changes from http to https and vice versa.
8. Set flags on cookies such as secure and HTTPOnly - when the secure flag is set cookies will only sent via SSL/TLS (HTTPS connections). When HTTPOnly flag is set, it prevent client side scripting which access cookies and its values. This helps prevent cross-site scripting and stealing session token stored in cookies. Path and domain attribute also can set appropriately.
9. Never to reuse session IDs - session IDs should not be used as cryptographic keys or create unique file names with it. These are only random identifiers assigned by application servers only for a particular session.
Different password cracking techniques
| Password cracking technique | Description |
| Social engineering attack (guessing and shoulder surfing) | This is a technique used to manipulate human into perform an action or divulge some confidential information without using any technical actions to breaking to systems. This technique can be utilized to attack systems without any technically sophisticated attacks. Two most interesting techniques are, shoulder surfing and guessing. For instance, you can pretend as a technical staff from the ISP and enter a office premises to meet the network administrator, and ask him to login to systems and see whether everything works perfectly. When network administrator types his password attacker can silently observe his password by standing behind the administrator and looking over his shoulder. Next option is to guess the password by profiling the organization and the user. Most users use a password relevant to them. Hence, if you know the person very well , chances are high to guess what he will use as a password. |
| Dictionary Attack | This is a subset of brute forcing attacks. Dictionary attacks try to use combination of words instead of all possible password combination of digits. Dictionary attacks use common usernames and passwords to crack passwords. This technique use dictionary words to guess passwords. |
| Brute Force Attacks | This method tries all possible combination of letters, numbers and characters until they find the correct combination. Comparatively this process takes long time depending on the length of the password, complexity, and the computer speed. |
| Hybrid Attack | This method of password cracking tries to add numbers or symbols to previous found passwords. Some cases users’ simply add new numbers or words to the end of old password and these passwords can be cracked easily. |
Subscribe to:
Posts (Atom)